
[ad_1]
Log4j was the bucket of cold h2o that woke up most builders to their software package offer chain safety problem.
We have invested a long time in program developing things and obsessing above our output atmosphere. But we’re creating on unpatched Jenkins packing containers sitting down under someone’s desk. We invest all this time guarding our runtimes, then deploy to them utilizing newbie tooling.
Our build environments are not approximately as safe as our generation environments.
That is what led to a entire good deal of superior-profile assaults in the very last 12 months, from SolarWinds, to the Codecov assault, to the Travis CI secrets leak. We’ve gotten so fantastic at defending our infrastructure that attackers looked for an much easier way in, and discovered it in the doorways we have left open in the provide chain.
Just cannot get in as a result of the perimeter security? Just obtain an open source dependency, or a library, and get in that way. Then pivot to all of the prospects. This is the present day software supply chain hack.
We need to have roots of have faith in for software
We have roots of trust for people right now. We have two-factor authentication, we have identification methods. These are factors to vouch for a person’s id. And hardware has the very same factor. We have encryption keys. We have hardware we can belief has not been tampered with when it boots up.
Even as online buyers we have roots of believe in. We have URIs, URNs, and URLs—effectively the namespaces on the online that join the identities, names, and spots of web sites we are browsing. SSL certificates tell our browsers that web pages are protected. DNS firewalls sit in between the user’s recursive resolvers to make confident our cache isn’t getting loaded with terrible requests. All of this is taking place driving the scenes, and has been extremely helpful in supporting billions of world wide web buyers for many years.
But we never have this for application artifacts currently.
Developers belief far too considerably implicitly
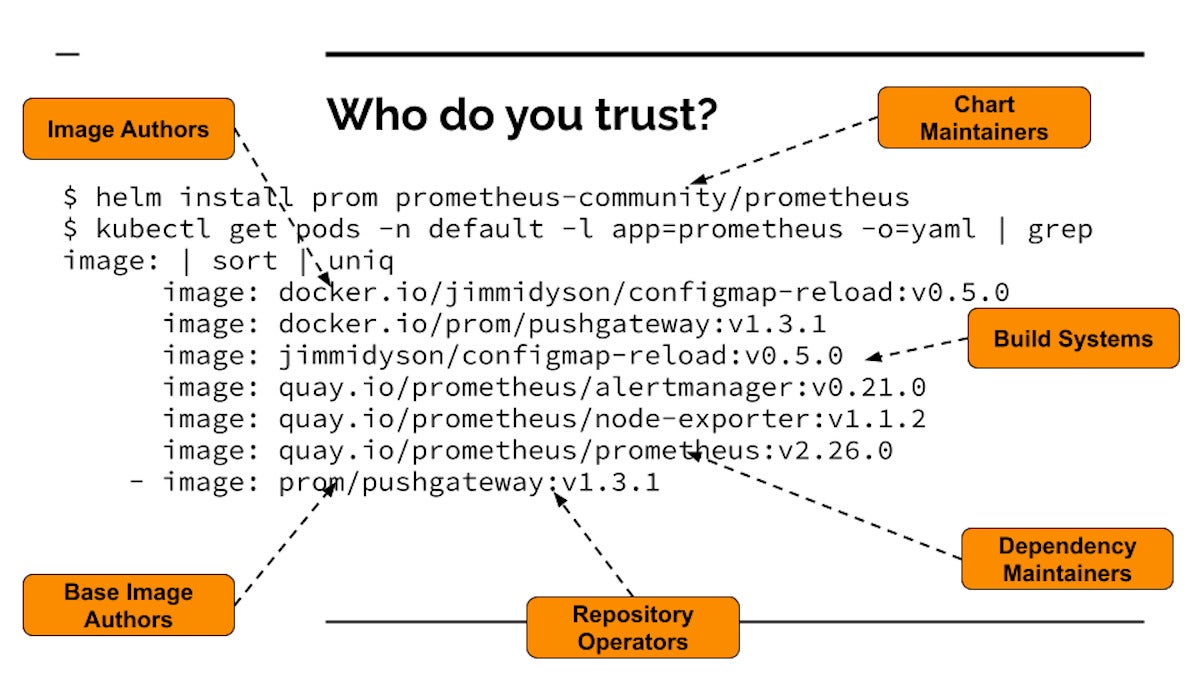
Get an function as commonplace as putting in Prometheus (a well-known open resource observability job) from the Cloud Native Computing Basis (CNCF) artifact hub. If you do your Helm install and then look at all the images that get pulled and start off running your cluster, you see many container visuals that end up managing from a straightforward installation. Builders are entrusting a full bunch of items to a complete bunch of diverse individuals and programs. Every single solitary just one of these could be tampered with or attacked, or could be destructive.
 Dan Lorenc
This is the reverse of Zero Trust—we’re trusting dozens of techniques that we really don’t know anything at all about. We do not know the authors, we do not know if the code is destructive, and for the reason that every impression has its personal artifacts, the full provide chain is recursive. So we’re not only trusting the artifacts, but also the people today who trusted the dependencies of these artifacts.
We’re also trusting the individuals who function the repositories. So if the repository operators get compromised, now the compromisers are component of your believe in circle. Any one controlling a single of these repositories could improve a little something and attack you.
Then there’s the make devices. Build units can get attacked and insert malicious code. That is accurately what transpired with SolarWinds. Even if you know and have faith in the operators of the visuals, and the folks working the devices that host the photos, if these are built insecurely, then some malware can get inserted. And yet again it’s recursive all the way down. The dependency maintainers, the create units they use, the artifact administrators that they are hosted on—they’re all undermined.
So when builders set up computer software deals, there are a large amount of things they are trusting implicitly, no matter whether they signify to have faith in them or not.
Computer software supply chain stability gotchas
The worst approach you can have in application provide chain safety is to do very little, which is what a good deal of builders are carrying out currently. They are making it possible for just about anything to operate on generation environments. If you have no security about what artifacts can run, then you have no plan exactly where they arrived from. This is the worst of the worst. This is not spending notice at all.
Enable-listing distinct tags is the next stage up. If you go through some of the tutorials all around most effective tactics with Kubernetes, this is very uncomplicated to set up. If you drive all your illustrations or photos to a single place, you can at minimum prohibit points to that place. Which is way far better than executing very little, but it’s however not excellent, mainly because then something that gets pushed there is now within your trust circle, inside of that barbed wire fence, and that is not really Zero Belief. Allow-listing unique repositories has all the same restrictions of make it possible for-listing precise tags.
Even the signing schemas in provide chain security are papering about the exact same challenge. Everything that will get signed now gets to operate, regardless of where it arrived from, which leads to tons of assaults tied to tricking anyone to signal the erroneous thing, or being unable to revoke a certificate.
Time to start asking the correct questions
Let’s say you’re walking down the sidewalk exterior of your office, and you obtain a USB thumb push sitting on the floor. I hope all people understands that you must definitely not acquire that generate within your place of work and plug it into your workstation. Anyone in computer software must (rightly) be screaming, “No!” Genuine attacks have occurred this way, and security orgs throughout the planet hammer this warning into all staff members as section of training.
But for some motive, we really do not even pause to imagine two times right before jogging docker pull or npm set up, even nevertheless these are arguably worse than plugging in a random USB stick. Both circumstances include getting code from somebody you do not trust and running it, but the Docker container or NPM deal will finally make it all the way into your manufacturing atmosphere!
The essence of this offer chain safety evolution is that as an market we’re relocating absent from trusting exactly where the software package artifacts arrive from, and investing significantly far more time figuring out roots of have faith in for what the artifact is.
Who posted this binary? How was it constructed? What model of the device was utilised? What source was it designed from? Who signed off on this code? Was just about anything tampered with? These are the ideal issues to be asking.
Subsequent 7 days, we’ll appear at the speedy-evolving open up source landscape that is forming a new stability stack for provide chain safety, and unpack important ideas developers need to understand—from roots of rely on, to provenance, to TPM (Trustworthy Platform Module) attestation.
Dan Lorenc is CEO and co-founder of Chainguard. Beforehand he was personnel software package engineer and guide for Google’s Open Source Protection Crew (GOSST). He has established jobs like Minikube, Skaffold, TektonCD, and Sigstore.
—
New Tech Discussion board presents a location to examine and focus on emerging company know-how in unparalleled depth and breadth. The collection is subjective, based on our choose of the technologies we imagine to be crucial and of finest fascination to InfoWorld viewers. InfoWorld does not acknowledge marketing and advertising collateral for publication and reserves the appropriate to edit all contributed articles. Mail all inquiries to [email protected].
Copyright © 2022 IDG Communications, Inc.
[ad_2]
Resource backlink
About the Author


